
OUR MISSION
Giving organizations back control over their digital identities.
Digital sovereignty is not just about where your data is hosted. It starts with a simpler question: who really controls your access?
With Vaultys, identities are no longer dependent on a fragile central point. Each user, machine, or agent can prove who they are—without passwords, without a single directory to compromise, and without surrendering control to a foreign infrastructure.
Digital dependency often begins with identity.
Every company today uses dozens of applications, accounts, cloud services, collaborative tools, and soon AI agents capable of acting independently.
But behind this complexity, one question is rarely asked: who truly holds the key to your access?
When all identities rely on a central directory or a single provider, security becomes dependent on a critical point. If this point is compromised, unavailable, misconfigured, or subject to external constraints, the entire organization can be exposed.
Sovereignty starts here: regaining control over identities even before talking about data.
What sovereignty means at Vaultys
Control
Your identities, your access, and your authentication proofs must remain under your control.
Vaultys enables organizations to maintain control over who accesses what, with what level of trust, and in which context.
Independence
Security should not depend on a single central provider.
Vaultys' decentralized approach reduces reliance on centralized architectures and limits critical points of failure.
Transparency
Sovereign technology must be understandable, auditable, and verifiable.
Vaultys relies on an open, auditable, and evidence-oriented approach, so that trust is not based solely on a promise.
No longer protect a central target. Remove the target.
Traditional models concentrate identities, access, and secrets in central systems. This approach sometimes simplifies administration, but it also creates a very high-value target for attackers.
Vaultys offers a different approach: distributing trust.
With VaultysID, each identity can carry its own cryptographic proof. VaultysHub then enables you to orchestrate access, applications, privileges, and usage without reverting to total dependence on a central directory.
6 pillars for actionable sovereignty.
Decentralized Identity
Each user, machine, or agent can have a verifiable identity, without relying solely on a central directory.
Passwordless
Eliminating passwords reduces exposure to phishing, credential sharing, and compromised access.
Open source & auditability
Trust must be verifiable. Sensitive technology should not operate as a black box.
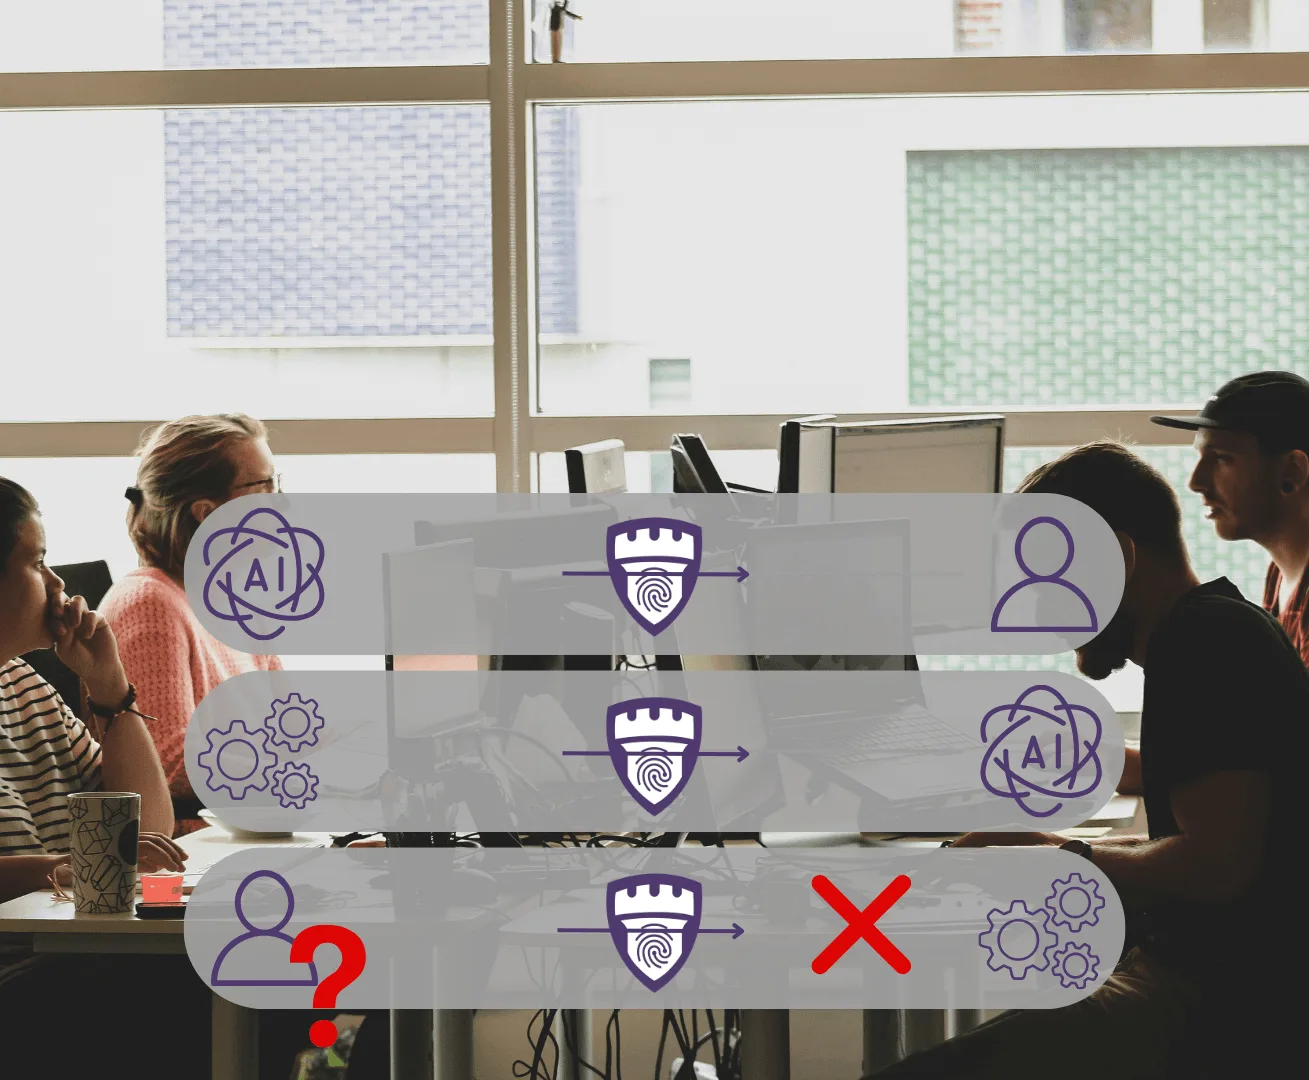
Access control
Organizations must know who is accessing what, with what level of authorization, and in what context.
Operational sovereignty
VaultysHub enables you to manage applications, Shadow IT, rights, privileges, and compliance evidence from an actionable interface.
Post-quantum resilience
Sovereignty must also anticipate future threats. Vaultys prepares identities and access to withstand tomorrow’s cryptographic developments.
Sovereignty must also anticipate future threats. Vaultys prepares identities and access to withstand tomorrow’s cryptographic developments.
Identities are becoming the new strategic territory.
Companies have never had so many identities to manage: employees, contractors, administrators, applications, APIs, machines, AI agents.
At the same time, attacks are becoming faster, more automated, and harder to contain. In this context, continuing to centralize everything in a single identity architecture creates a major point of dependency.
Sovereignty is therefore not an abstract concept. It is a condition for resilience.
Concretely, regaining control means
Know who accesses what
A clear view of users, applications, services, and connected agents.
Reduce invisible access
Detection of Shadow IT, orphan accounts, and uncontrolled usage.
Eliminate the password as a weak point
Passwordless authentication via VaultysID, passkeys, biometrics, or FIDO2 keys.
Decentralize trust
Identities that can be verified directly, without relying on a single central point.
Generate evidence
Actionable reports for audits, compliance, and security reviews.
Sovereignty should no longer be a promise. It must become an architecture
"Digital trust can no longer rely on a single central point. At Vaultys, we are building an approach where every identity can be verified, every access can be controlled, and every organization can regain control over its security.
Our mission is simple: to make authentication safer, more sovereign, and more natural to use—without passwords, without fragile dependencies, and without compromising the user experience."
François-Xavier Thoorens
Co-founder & CEO of Vaultys
A mission driven by three solutions.
products
VaultysHub
Regain control over access.
Centralize applications, detect Shadow IT, automate onboarding and offboarding, and generate actionable evidence.
VaultysID
Carry sovereign identity.
Assign each user, machine, or service a decentralized, verifiable, and passwordless identity.
VaultysClaw
Supervise autonomous agents.
The first P2P authentication platform dedicated to agentic AI. Give each agent a cryptographic identity, block Shadow AI, trace every action, and cut access with a single click (kill-switch).